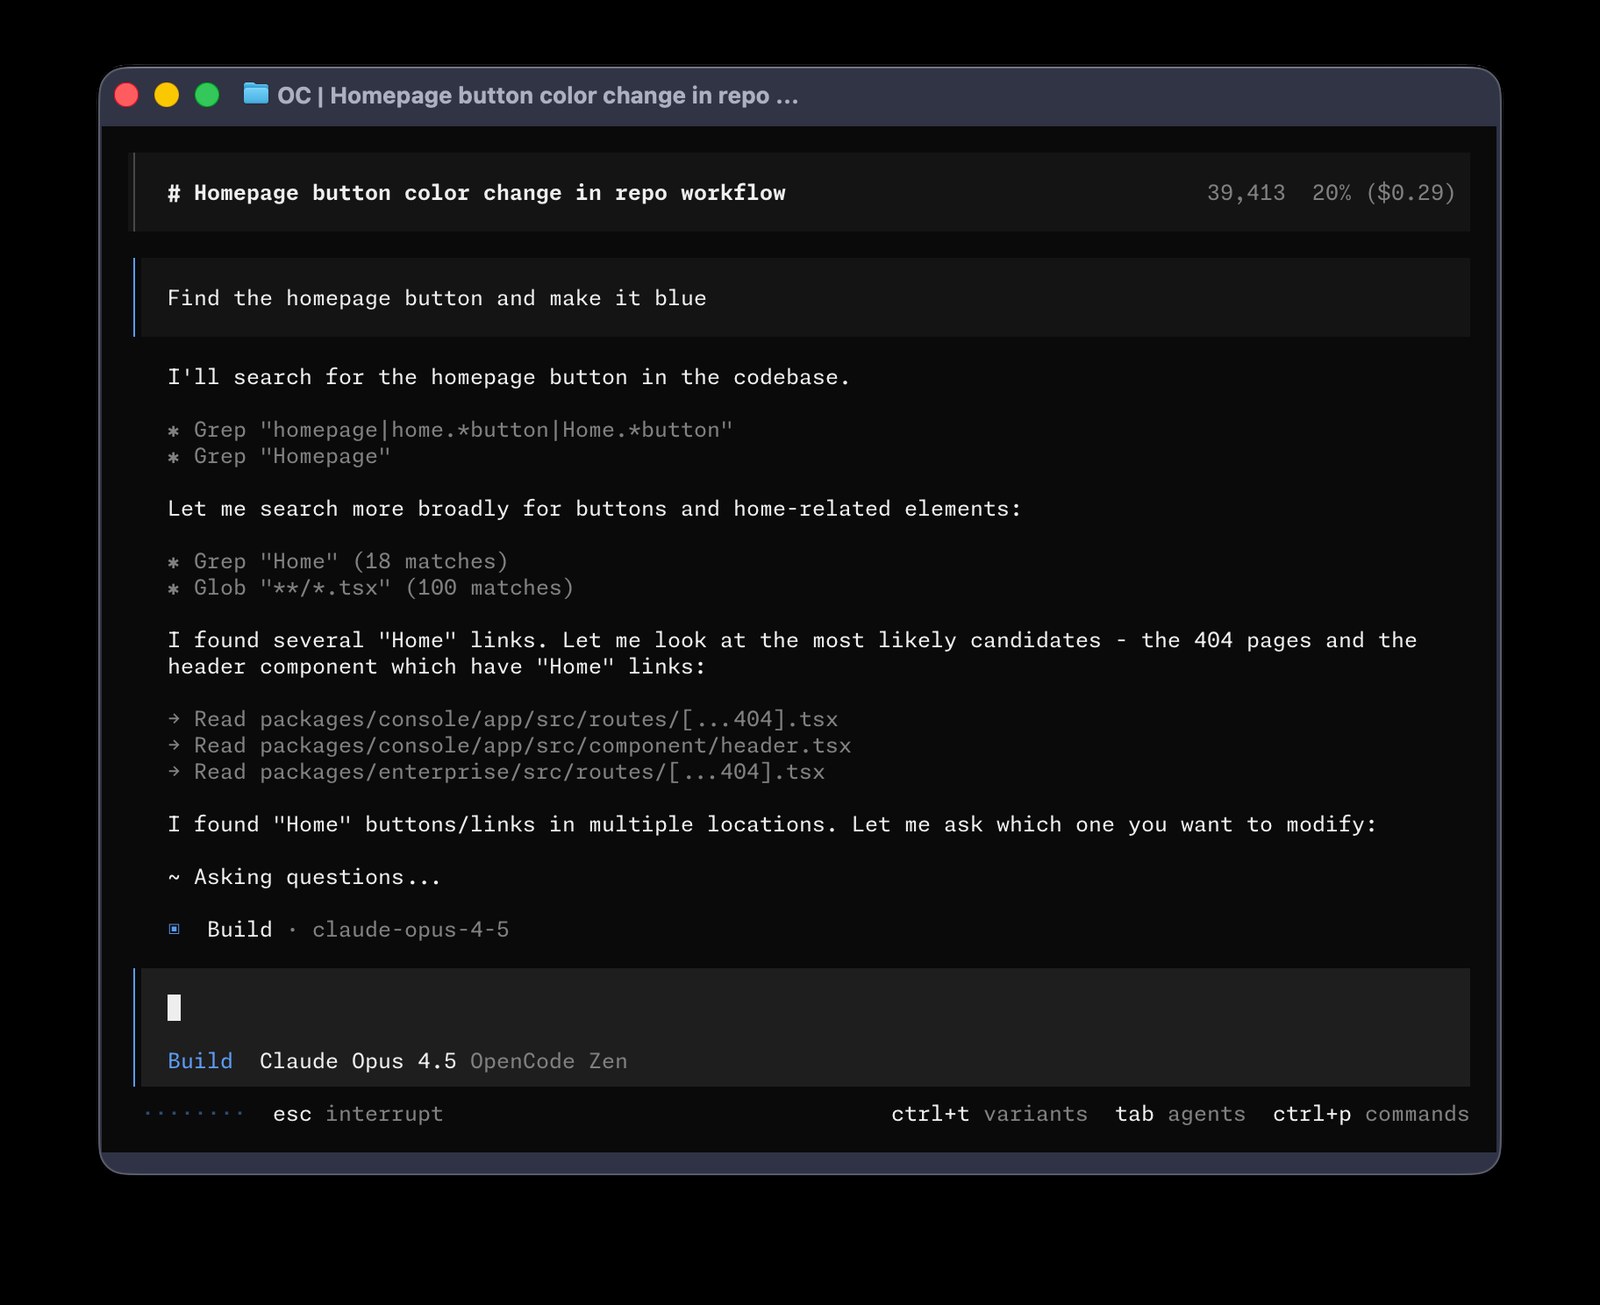
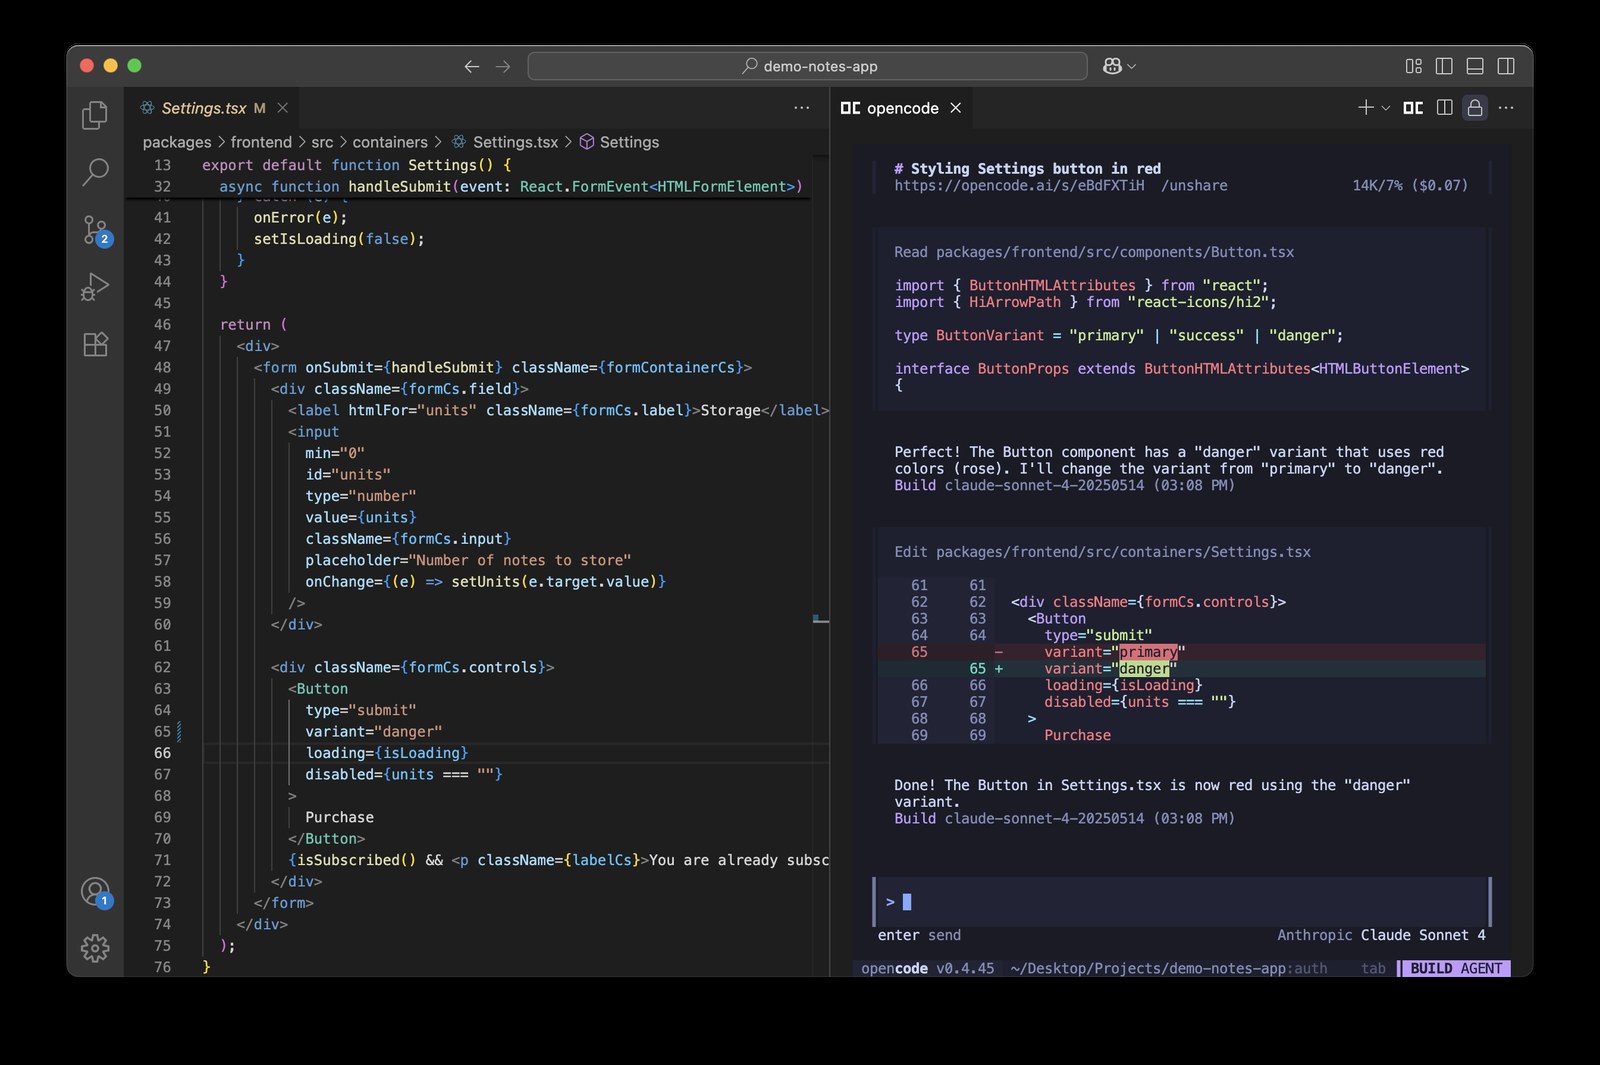
OpenCode, an open-source AI coding agent that runs in the terminal, code editors and a desktop app, says that on the night of Friday, October 16, someone broke into a legacy system it was in the process of shutting down. The intruder may have reached the OpenAI, Anthropic and Google API keys that some customers had stored in OpenCode Console, the paid web service that calls those providers' models on a team's behalf. The company says 1.4% of Console users are affected, all of them with an outside provider connected, and that each of them got an email. If you didn't get one, OpenCode says you're in the clear.
Some of those users have already found charges they didn't make. Colin Parsons posted on X that someone ran up $281 on his OpenAI key and $168 on his Anthropic key starting at 2 a.m. ET on Saturday, The Latent reported. Another user, Preston Zeller, put his losses at $1,700. Those numbers come from users, and OpenCode hasn't given a total.
Why a stolen API key can spend your money
An API key is a long password that software sends to OpenAI, Anthropic or Google every time it asks one of their models for an answer. The provider doesn't check who is sending it. If the key is valid, the model answers and the owner's account gets billed. Usage is counted in tokens, the chunks of text a model reads and writes, and priced per million. So anyone holding a copy of your key can keep spending on your account until the key is revoked or a spending cap kicks in.
Console kept these keys on OpenCode's servers so team members could use the models without ever seeing them. When someone sends a request, Console attaches the key before passing it on to the provider, according to OpenCode's documentation. That store of keys is what the company believes may have been exposed.
What OpenCode hasn't explained
OpenCode said the breach was related to a "large scale distillation attack" without saying how. Distillation means training one model on the answers of a stronger one. That takes millions of queries, and someone has to pay for them. With stolen keys, the bill lands on the keys' owners. TechCrunch notes that skeptics see a fairly ordinary credential theft and that any use for distillation is unproven.
The company hasn't said how the attacker got in, how the keys were stored, how many people that 1.4% represents or whether every exposed key was actually used. On Saturday it said the incident was still ongoing.
What to do if you got the email
The email, with the subject line "Action Required: Potential provider key breach," tells users to revoke each key in the provider's own dashboard and create a new one. Deleting it from Console isn't enough, because the key keeps working at OpenAI, Anthropic or Google until they revoke it, as The Hacker News explains. Then put the new key into every app and script that used the old one, and go through each provider's usage logs back to October 16 for requests you don't recognize.
As for the money, Anthropic and Google blocked the keys they believed were exposed, OpenAI says it will refund API credits used in the attack, and OpenCode says refunds for unauthorized charges are underway, according to TechCrunch. Going forward, set a spending limit or alert on each account and give each tool its own key, so a leak can be shut off without touching the others.
If you use OpenCode in the terminal, an editor or the desktop app without Console, you're not affected, the company says. Those versions store keys on your own machine, and co-founder Dax Raad wrote that "those keys never come to us." Because the problem sat on Console's servers, there's no patched version to install.
AI models balked at helping the defense
Attackers kept trying to get back in for about 48 hours, and OpenCode had AI agents watching its systems around the clock. Raad said commercial models stopped helping when the malicious code they were analyzing set off their safety filters, TechCrunch reported. Things improved once OpenAI gave the team access to Daybreak Blue, a program that lets vetted security teams get fewer refusals. Hugging Face hit the same wall in July while investigating OpenAI models that broke into its systems.
The conversation starts here
Sign in with a supporter account to comment. Sign in
Nobody has commented yet. Want to go first?